Sentinel workspace, data connectors, and log sources
Cloud SIEM track
Microsoft Azure Sentinel Training
Learn how a cloud SIEM supports detection and investigation. The focus stays on the analyst workflow, not memorising a portal.
Two live one-hour classes free. Payment begins on day 3 only if you decide to continue.
BAIC · CLOUD, OBSERVABILITY & SECURITY
Explore practical guides and specialist modules for the systems and incidents you work on.
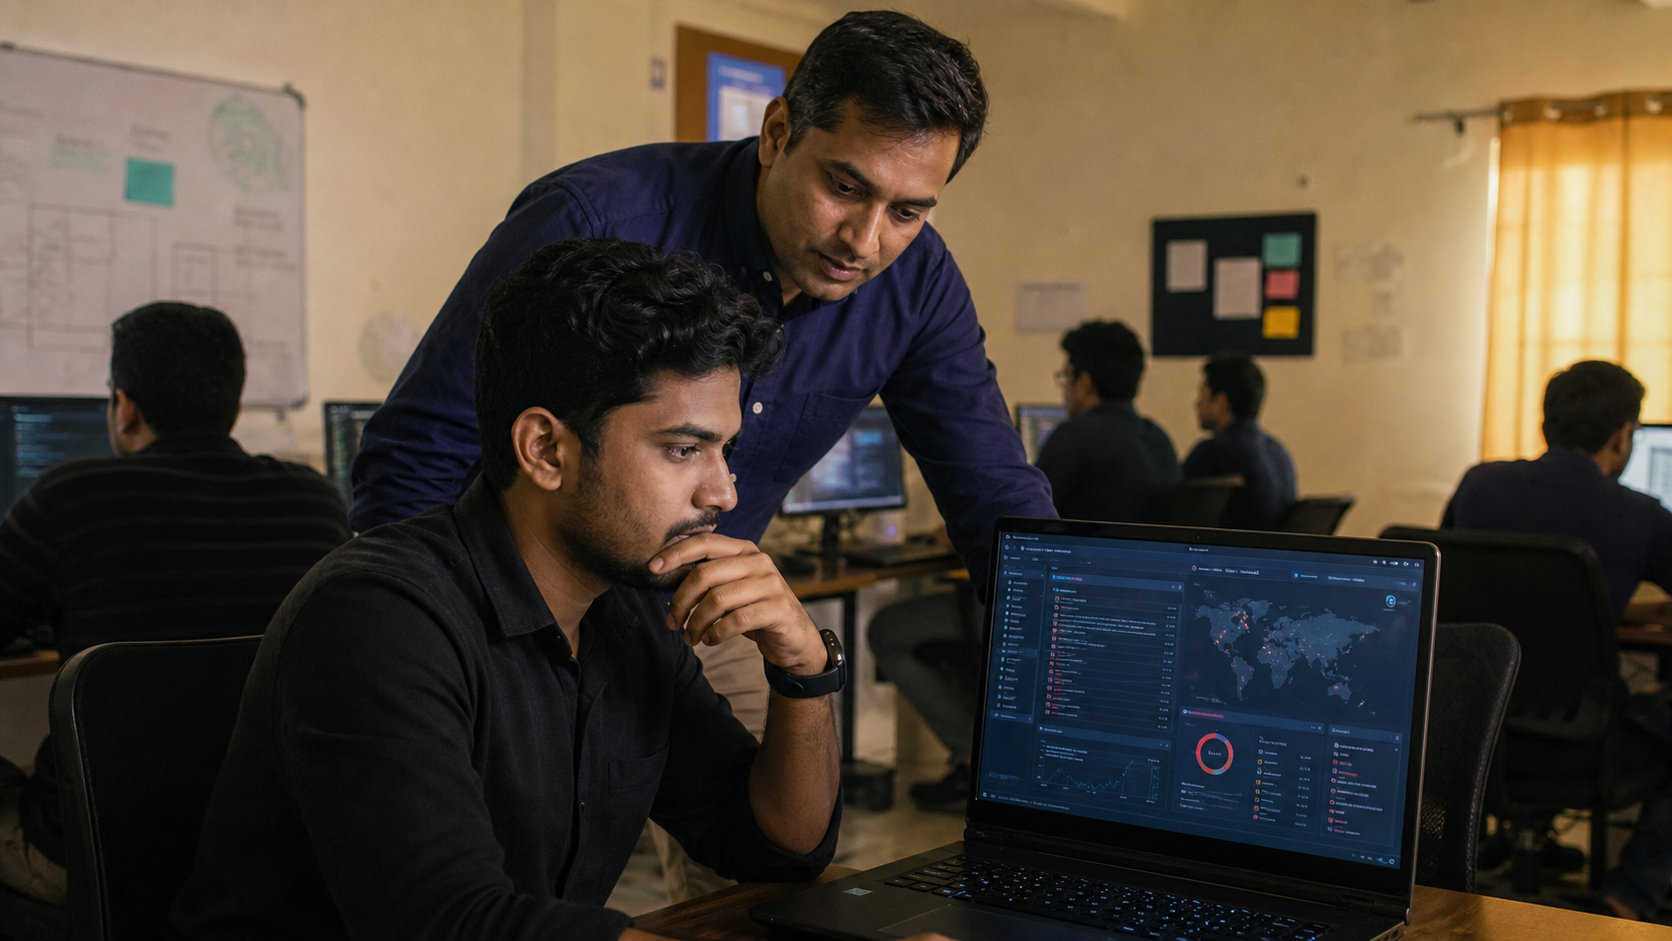
Explore observability guides →SECURITY OPERATIONS LABIllustrative workflow
Explore each step
82%Placement rate
100+students trained
2 free classesbefore any payment decision
Who this is for
A practical path, not a certificate-only course.
Learners targeting cloud security, SOC, and Microsoft security operations roles.
What you practise
Build skills employers can discuss with you.
Analytics rules, incidents, entities, and investigation workflow
KQL foundations and query interpretation
Automation context, interview practice, and role-specific resume work
Job readiness
Show your work in a clear, credible way.
- Navigate an incident investigation
- Read and adapt basic KQL queries
- Describe Sentinel use cases with confidence
Related paths
Compare the next useful course.
Next-Generation SOC Analyst Training with AI
Build the working habits needed for a security operations role: read alerts, separate useful signals from noise, investigate with care, and explain your decisions clearly.
splunk siem training
Explore this related BuildAI Careers path.
Cortex XSOAR Training
Understand how security teams reduce repetitive response work with disciplined playbooks, integrations, and clear escalation paths.
Identity and Access Management Training
Learn the decisions behind access: who needs it, how it is approved, when it changes, and how teams keep a defensible record.